
5 Steps to Audit Ready Compliance Dashboards for Compliance Teams
Short answer
A compliance dashboard should answer a defined question and link back to the records behind it. Give a board a small view of material risks and open actions; give an auditor the source, owner and date for each reported control.
A compliance dashboard should answer a defined question and link back to the records behind it. Give a board a small view of material risks and open actions; give an auditor the source, owner and date for each reported control.
TL;DR:
- Different stakeholder roles require customized views, with board members needing high-level risk summaries and auditors requiring detailed evidence links.
- Metrics should focus on control and evidence coverage, openness of findings, and third-party compliance, with evidence health prioritized as a separate KPI.
- Data sources like HRIS, ticketing, SIEM, and IAM systems must be integrated through reliable connectors, with data quality checks ensuring accuracy and completeness.
- Effective dashboards maintain role-based, toggleable views, clear labeling of timeframes, and a minimal set of key indicators to avoid overload and confusion.
- Successful implementation hinges on mapping workflows first, running small pilots with human review, and establishing governance practices before automating data collection or updates.
Table of Contents
- What do compliance dashboards actually show different audiences?
- What metrics belong on a compliance dashboard?
- Which systems should feed a compliance dashboard?
- How should a compliance dashboard be laid out?
- How do you actually implement a compliance dashboard?
- What goes wrong with compliance dashboards, and how do you prevent it?
- How do you know a compliance dashboard is actually working?
- How I think about compliance dashboard projects
- How Pattrn Data helps you build compliance dashboards you can trust
- Sources
What do compliance dashboards actually show different audiences?
Start each view with the decision it supports. A board view can show material exposure and overdue actions; an operational view can show controls needing attention; an audit view can link a finding to its owner, source record and review date. Keep the underlying definitions visible so the views can be reconciled.
Separate the views without giving the same control conflicting definitions. Record which filters, dates and evidence sources each audience sees.
- Board or executive view: answers “are we exposed to material risk right now?” using a small set of readiness scores, trend arrows and red/amber/green summaries. No raw incident logs, no ticket queues.
- Operational view: answers “what needs attention today?” with control health scores, open remediation items, and workload by owner.
- Audit-flight view: answers “can we prove this control worked, and where is the evidence?” with active findings, remediation packets and evidence links attached to each item.
Toggleable or filtered views let one underlying data set serve all three audiences without duplicating infrastructure. A compliance platform built this way lets an operational lead flip a segment filter and see the same data an auditor is reviewing, filtered down to their remit, rather than maintaining three separate spreadsheets that inevitably drift apart. Research into dashboard modules confirms this separation matters in practice: effective platforms keep programme-health views distinct from audit-flight views, using toggles rather than merging operational noise with governance signal.
Choose a summary measure only if its calculation and limitations can be explained. A single readiness score can hide a control with missing evidence, so let the reader inspect the underlying status and unresolved gaps. Distinguish a control that failed from one that has not been checked.
What metrics belong on a compliance dashboard?
Use the categories below as a starting checklist, then select measures that answer your actual oversight questions. For each measure, record its definition, owner, denominator and source rather than relying on a familiar dashboard label.
- Control coverage and control effectiveness: what percentage of mapped controls are tested, and of those tested, what percentage passed. A control that has not been tested in six months should not show green.
- Evidence coverage and evidence health: whether every control has a linked evidence artefact, and whether that evidence is current, complete and correctly tagged.
- Outstanding findings and remediation timelines: open findings by severity, age, and owner, plus mean time to remediate (MTTR) as a trend line rather than a single snapshot.
- Policy attestations and training completion: the percentage of staff who have signed off on current policy versions and completed mandatory training, broken down by department.
- Incident and near-miss counts: tracked separately from findings, since an incident reflects something that already happened rather than a control gap identified proactively.
- Third-party and vendor compliance status: increasingly material for enterprise compliance solutions where supply-chain obligations sit outside the organisation’s direct control.
Pro Tip: Show evidence health as its own metric, separate from control effectiveness. A control can be “effective” on paper while its supporting evidence is six months stale, and that gap is exactly what auditors probe first.
Separate evidence coverage from the assessment of a control. Record whether the evidence exists, when it was collected and which control version it supports. A green status without retrievable supporting records should remain a visible review question.
Choose counts, percentages and trends to suit the question. Show the denominator beside a percentage and label the reporting period on every chart. Where periods differ, explain why rather than inviting a comparison between unlike figures.
Which systems should feed a compliance dashboard?
Inventory the systems that hold the records for your selected controls. Use the categories below to find potential sources, then identify the actual record owner, update frequency and known gaps before connecting anything.
- HRIS systems supply training completion, role changes and starter/leaver data, which underpin attestation tracking and access reviews.
- Ticketing and case management platforms supply remediation status, finding ownership and time-to-resolution data, usually the richest source for operational metrics.
- SIEM and security monitoring tools supply control-triggering events for technical controls, which matters most for data compliance dashboards tracking access and breach-adjacent activity.
- IAM and contract management systems supply access-entitlement evidence and third-party obligation tracking, both frequent audit-sampling targets.
How those systems connect matters as much as which systems connect. API syncs work well for near-real-time updates where the source system exposes a stable interface. Scheduled ETL jobs suit systems that update in batches, such as nightly HR exports, and remain the most dependable pattern where a vendor has no usable API. Event streams fit high-volume, low-latency needs like SIEM alerts. Agent-based pulls fill gaps where none of the above exist, at the cost of more maintenance overhead. A data layer built for real-time reporting rather than batch-only exports tends to age better as obligations expand.
Data quality checks matter more here than in almost any other reporting context, because a wrong figure on a compliance dashboard is not a cosmetic error, it is a misrepresentation to a regulator or a board. Before any source goes live, confirm four things: every record carries a canonical ID that maps cleanly to a control or obligation; every event carries a reliable timestamp; every data point has a named owner accountable for its accuracy; and completeness gaps are visible rather than silently defaulting to zero. Mapping controls to source events once, and reusing that mapping across frameworks, avoids the common trap of duplicated indicators that quietly disagree with each other. Reusing mapped evidence across frameworks instead of rebuilding it per audit is one of the more reliable ways to cut manual prep time.
How should a compliance dashboard be laid out?
Lay out each screen around its audience and the decisions they need to make. Keep the path from a summary indicator to its supporting records visible.
For a board view, select a small set of material indicators rather than filling every available chart slot. Open findings, evidence coverage and control trends may be useful, but each needs a definition, reporting date and route to the underlying records. Include unresolved data gaps alongside the headline status.
- Keep the executive layer static and load-bearing; put everything exploratory behind a drill-down.
- Give investigators and auditors a path from any summary figure straight to the underlying evidence packet, ideally in two clicks or fewer.
- Never merge programme-health metrics (ongoing controls, training, attestations) with incident-resolution detail on the same screen; use tabs or toggles instead.
- Apply one colour meaning across every screen: red always means the same severity of problem, whether it is a control or a finding.
- Attach ownership metadata to every widget, so a viewer always knows who to ask when a number looks wrong.
Keep ongoing control status distinguishable from findings raised in a particular audit. A filtered view may be sufficient; a separate dashboard may be justified where access or reporting needs differ. Check that both still refer to the same control and evidence definitions.
Pro Tip: Label every time window explicitly on the screen itself, not just in a hidden filter setting. “Last 90 days” printed on the chart avoids the argument that happens three months later when someone assumes a figure covers the full year.
Check the displayed dates, filters and definitions before distributing a report. Preserve that context in an export so a later reader can tell which period and population each figure describes.
How do you actually implement a compliance dashboard?
Most compliance dashboard projects fail for a reason that has nothing to do with software choice: the underlying workflow was never mapped, so the dashboard faithfully displays a broken process. Building dashboards before mapping the compliance workflow is the single most common cause of dashboards nobody trusts. A five-step sequence avoids that trap.
- Map the workflow and the evidence lifecycle first. Before selecting a single KPI, document how a control is tested, who signs it off, where evidence lands, and how a finding moves from open to closed. This is the step most teams skip, and the one that determines whether everything built afterwards is trustworthy.
- Define data boundaries and canonical identifiers, and assign named owners. Every metric needs one accountable person, not a team distribution list. Decide upfront which systems are the source of truth for which fields, and resist the temptation to let two systems both claim ownership of the same figure.
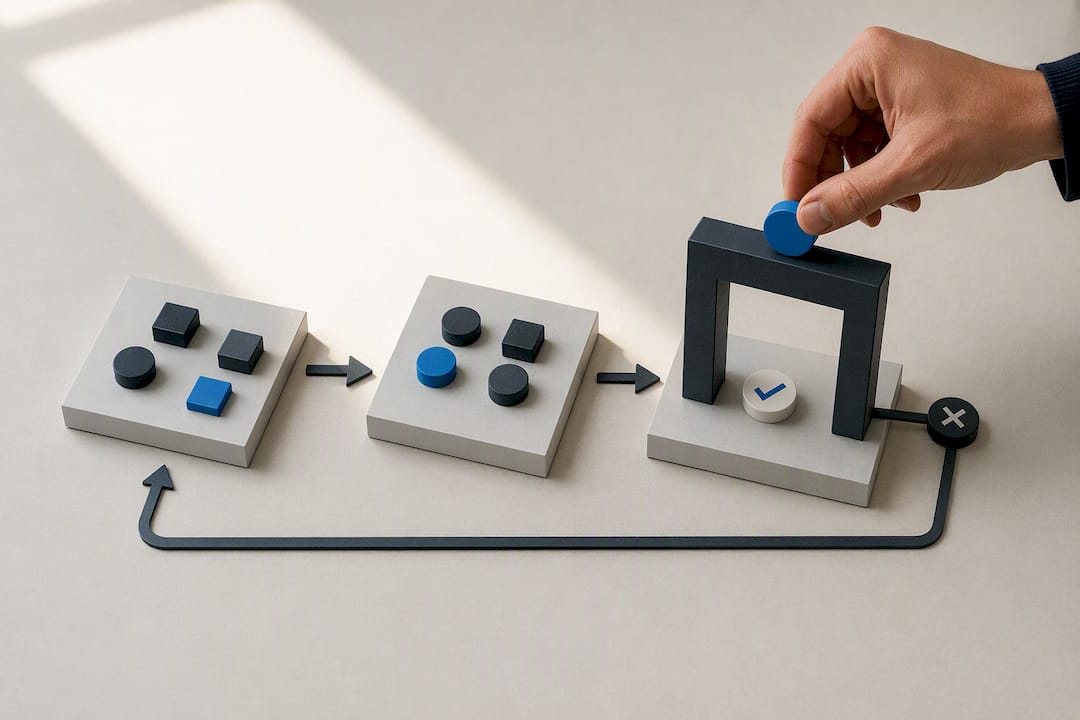
- Run a small pilot with approval gates and human review at every decision point. Pick one control family or one business unit, not the whole organisation. Build in explicit checkpoints where a person, not a rule, decides whether a status changes.
- Introduce automation for collection and notification, not for judgement. Automated pulls and alerts save real time. Automated conclusions about whether a control passed do not belong in a first release, and arguably never should without a human sign-off attached.
- Scale with change control, an audit trail, and a fixed review cadence. Every rule change needs a record of who approved it and why, with a documented rollback path.
This sequencing mirrors what the Pattrn Protocol applies across AI and automation projects generally: map the workflow, set data boundaries, keep human review in place, then automate what is safe to automate. It is the same discipline that governs audit trail design for AI-assisted workflows, just applied specifically to compliance evidence.
Pro Tip: Pilot on a control family with known evidence gaps and an available owner. Test whether the dashboard exposes those gaps and whether a reviewer can retrieve the supporting records. Passing that test does not establish coverage for other controls.
Keeping humans accountable for judgement matters most where AI enters the picture. AI can summarise regulatory updates or flag overlapping obligations across frameworks efficiently, but responsibility for interpreting and acting on those updates has to stay with a named reviewer, not a model. The same principle holds for pilots involving automated monitoring more broadly: incremental rollouts with defined human checkpoints at each stage reduce the risk of an automated rule making a call nobody signed off on.
What goes wrong with compliance dashboards, and how do you prevent it?
Use the failure patterns below as review prompts, not as an exhaustive list. For each one, ask how your dashboard would expose the problem and who would investigate it.
- Treating the dashboard as the fix rather than the output. A dashboard built on top of an undocumented, inconsistent process will faithfully report that inconsistency. Fix the workflow before building the screen, not after.
- Over-customising early and accumulating maintenance debt. Bespoke builds for every stakeholder request feel responsive at first and become unmaintainable within two release cycles. Configurable, role-based views with filters cost less to run than five separate custom dashboards.
- Match update cadence to the decision. For each control, agree the freshness needed, the source delay, the cost and who responds to stale data. Test the chosen cadence rather than assuming real-time updates are always necessary or a periodic snapshot is always sufficient.
- Inconsistent or missing evidence taxonomy. If evidence types, timestamps and owners are not standardised from day one, every widget that links to “supporting evidence” becomes a manual reconciliation exercise later.
- Weak governance around access and change. Without a change log, an audit review schedule, and clear access rights by role, a dashboard that started accurate drifts silently until someone notices during an actual audit.
Assign an owner to each metric, source mapping and exception route. Review those responsibilities when a source system, control or team changes; adding another chart will not resolve an undefined decision right.
How do you know a compliance dashboard is actually working?
Test whether the dashboard supports real oversight tasks: finding an overdue action, checking the records behind a status, and identifying who must resolve a gap. Record what the reviewer could and could not establish.
- Adoption and engagement: how many distinct viewers check the dashboard weekly, and what proportion of sessions include a drill-down rather than a glance at the summary screen.
- Operational impact: measurable reduction in audit preparation hours and fewer ad hoc data requests landing on the compliance team’s desk before board meetings.
- Process metrics over time: MTTR for remediation trending down, and evidence completeness trending up, both tracked on the same rolling window used elsewhere on the dashboard.
- Stakeholder confidence: whether the board is asking fewer clarifying questions about the numbers themselves and more questions about what to do next.
Statistic to note: teams that pair real-time dashboards with an exportable executive summary report measurably shorter board meeting time spent on compliance topics, because the numbers arrive pre-digested rather than debated live. Executive summaries built into the dashboard itself shift board time from data-checking to decision-making.
Set review intervals to match the pace of control and source changes. Review operational exceptions with their owners and revisit the reporting model when definitions, systems or obligations change. A calendar check is useful only if someone can act on the findings.
How I think about compliance dashboard projects
Start with the finding lifecycle: who raises it, what evidence supports it, who can close it and how that decision is recorded. Use a sample finding to test that path before choosing chart types.
The pattern that keeps showing up in dashboard work generally, well beyond compliance specifically, is that small, approval-led pilots outperform ambitious full rollouts. A pilot on one control family, with a named owner and a human checkpoint at every decision, tells you more in six weeks than a full enterprise deployment tells you in six months. Case studies from wider automation projects show the same pattern: clearer ownership and tighter follow-up loops tend to matter more than the sophistication of the tooling itself.
If AI helps summarise updates or flag possible evidence gaps, show the material for a named reviewer to check. Keep the decision about a control separate from the generated summary.
Rohit
How Pattrn Data helps you build compliance dashboards you can trust
Pattrn Data is the practical route to a compliance dashboard that survives audit scrutiny, without the maintenance debt of a fully bespoke build or the risk of automation making calls nobody approved. Where a generic BI project starts with chart types, we start with your evidence lifecycle and control ownership, because that is what a dashboard actually has to reflect.

Our AI clarity sessions map your compliance workflow before anything gets built, so the dashboard reflects a process you would defend to a regulator, not one nobody has documented. From there, a fixed-price pilot implementation covers one control family with approval gates and human review at every decision point, and an ongoing governance retainer keeps the audit trail, access rights and review cadence current as obligations change. This is the same territory covered in our guidance on connecting AI tools to existing access controls, applied specifically to compliance reporting.
If your current setup is scattered spreadsheets, unclear metric ownership, or automation nobody fully trusts, start with our AI implementation service to scope a pilot around your highest-risk control family.
Sources
For teams researching the technical side of implementation, a handful of sources are worth bookmarking. Fanruan’s explainer on compliance dashboard mechanics covers the workflow-first argument in more depth. AesirX’s dashboard module documentation is a useful reference for how programme-health and audit-flight views separate in practice. Resolver’s compliance management overview is a solid starting point for evidence-health scoring methods, and Compyl’s compliance platform documentation covers evidence taxonomy design in more technical detail than most vendor sites attempt.
Recommended
Related services
AI governance consulting
Create policies, approval routes, ownership and controls that teams can actually use day to day.
AI governance consultingAI Risk & Efficiency Audit
Map real workflows, AI use, data exposure, opportunity value and governance controls before buying or building more tools.
book the AI Risk & Efficiency AuditAI workflow automation
Turn repeatable admin, client service and reporting work into controlled workflows with clear human review points.
AI workflow automation support