
Professional Firms: Map Workflows First for Power Automate Governance
Short answer
Start Power Automate governance by inventorying the flows that touch client or regulated work, naming an owner for each, and checking its connector and data boundary before adding more automation.
Start Power Automate governance by inventorying the flows that touch client or regulated work, naming an owner for each, and checking its connector and data boundary before adding more automation.
TL;DR:
- Review production-environment access after mapping critical workflows; record the ownership and data boundaries that need checking.
- Define who administers environments, builds flows and runs them, then check the actual access granted.
- Consider separate development, test, production and exploratory work, with access and data policies checked for each.
- Review flow activity, ownership and capacity against agreed criteria before deciding what to change or retire.
- Consider whether a Centre of Excellence adds useful inventory, ownership and follow-up records, and who will maintain it.
Table of Contents
- What is power automate governance and why does it matter?
- Permissions and roles: makers, run-only users and security groups
- How should environments and DLP policies be structured?
- What should you monitor and when should flows be retired?
- How do you keep flows maintainable over time?
- What role does a Centre of Excellence play in governance?
- Pattrn Protocol in practice: mapping, piloting, scaling
- Author perspective: balancing control and productivity
- How Pattrn Data helps you build lasting governance
- Sources
What is power automate governance and why does it matter?
Power Automate governance brings together flow ownership, permissions, data policies and review. Use the linked governance overview and strategy as a reference when deciding how those arrangements fit the firm's flows. A policy or admin tool alone does not establish that the estate is secure or compliant.
For a professional services firm, the objectives are:
- Security: define who may create, share and run automation against client or financial data.
- Compliance: keep relevant approval and data-access records, and check which requirements apply.
- Scalability: decide how additional flows will be approved and maintained.
- Cost control: review licences and connector use against the work in scope.
- Maintainability: document ownership, dependencies and support when staff roles change.
Choose how approval and administration are divided. A centralised model keeps decisions with IT or a governance lead; a federated model shares defined responsibilities with departmental admins; a decentralised model needs clear boundaries too. Decide which platform, environment, support and account responsibilities are needed rather than assuming every firm needs a Centre of Excellence.
Permissions and roles: makers, run-only users and security groups
Check who can build, own and run each flow. Distinguish those tasks before granting access, and review the permissions actually available for the environment and flow.
Use the following questions to plan the permission structure, checking the platform's supported roles and settings before implementation:
- Check the available environment-administration, maker and run-only permissions; do not assume they are all equivalent Dataverse roles.
- Check whether an environment security group fits the access design, and test how membership affects access.
- Where supported, consider groups for run-only and co-owner access, and test how access is revoked.
- Agree who needs ownership rights and how ownership survives staff changes. Check the licensing, access and support implications before choosing an account arrangement.
- Document the criteria for approving a new maker and the triggers that revoke access (role change, leaver, incident).
Review reminder: set an access-review schedule around role changes, leavers and incidents. Record findings and unresolved access.
How should environments and DLP policies be structured?
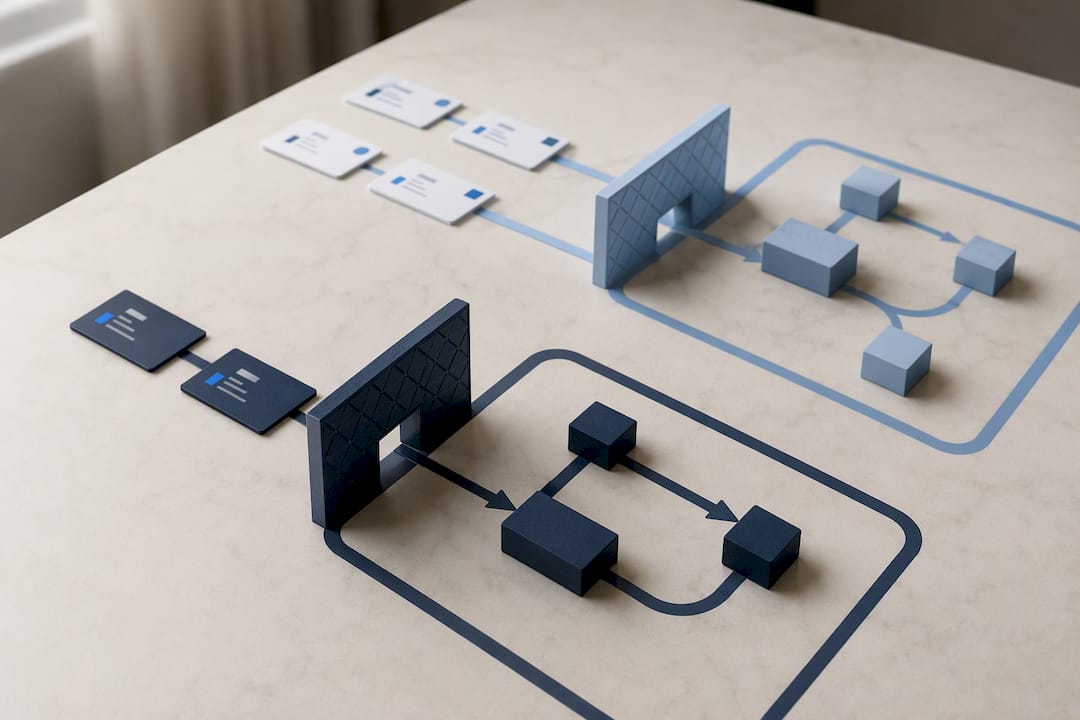
Review environment boundaries alongside data loss prevention (DLP) policies. Check which connector classifications and policy scope apply to the actual flows, then test the relevant data paths. Neither the proposed layout nor a policy label is evidence that leakage is prevented.
Possible design points to check are:
- Development and test environments with access and test data separated from live client work as agreed.
- A production environment with named owners and an access design that has been checked.
- A sandbox for genuinely exploratory work, kept separate from anything touching client identifiers.
- DLP policy scope and connector rules checked against the flows and environments in use.
Check the scope and effect of each DLP policy rather than assuming a tenant-wide policy covers every flow as intended. The linked data integration approach is a related service route; it is not evidence that a particular classification is correct.
What should you monitor and when should flows be retired?
Agree what flow activity, failures, ownership changes, connector use and capacity need review, who reviews them and what triggers action.
Build these into practice:
- Consider an owner-change alert where the platform supports it, then test the recipient, coverage and escalation route.
- Set failure-alert thresholds for the flow and review their results; a threshold may miss relevant individual failures.
- Agree an inactivity-review period for the use, and check dependencies before marking an apparently unused flow for retirement.
- Route flagged flows through an owner approval step before archiving, and take a backup before deletion.
- Agree a schedule for reviewing licensing and capacity against the flows in use.
How do you keep flows maintainable over time?
Keep documentation and support arrangements that let an authorised colleague review or change the flow. Check the relevant coding guidance against the platform features in use.
- Review whether splitting a complex flow makes its logic easier to test and maintain; check dependencies before using child flows.
- Use consistent naming conventions for flows, connections and variables, so anyone opening a flow six months later can follow it without a walkthrough.
- Check how environment variables and connection references are supported for the deployment, and keep credentials out of source configuration. Test movement between environments rather than assuming it works.
- Build explicit error handling (Try/Catch/Finally patterns) rather than letting failures fail silently.
- Test trigger and concurrency settings against the expected workload and service limits.
- Check which flow-checking tools are available and appropriate, and record their findings. Include an authorised peer review where the firm's approval arrangements call for one.
Review reminder: ask an authorised colleague to explain the flow's purpose, dependencies and error handling, and resolve any gaps before the release decision.
What role does a Centre of Excellence play in governance?
A Centre of Excellence (CoE) can be considered as an operating arrangement for inventory, administration and review. Check the actual components, their coverage and who maintains them; do not assume that installing them enforces policy or detects every risk.
Possible components to assess are:
- Inventory and explorer views with defined coverage of flows, owners, connectors and activity.
- Inactivity and owner-change checks whose coverage, recipients and follow-up arrangements have been tested.
- Metadata records for business unit, data sensitivity and approval status where those fields support the review.
Use inventory and monitoring findings to decide what needs review. A change in connector use may call for a policy check, and capacity findings may call for a licensing review; record the decision and supporting evidence.
Pattrn Protocol in practice: mapping, piloting, scaling
Map the work before choosing the tooling. The linked Pattrn Protocol case study is a reference to examine, not verification that this sequence succeeds for every firm.
- Map first. Document the workflow and every point where a human makes a judgement call, not just where data moves. Flag data boundaries explicitly, especially anywhere client or regulated data crosses a system.
- Pilot small. Agree the environment, maker access, data policy and monitoring for a narrow use, and test them before widening the pilot.
- Operationalise deliberately. Keep a runbook and agree ownership, review and retirement arrangements. Decide whether to expand from the pilot evidence and unresolved issues, not a universal review-cycle rule.
Check whether DORA and other applicable frameworks affect the process before describing a control or audit trail as a requirement.
Author perspective: balancing control and productivity
I would start with a narrow pilot and identify the data boundaries and human decisions before adding tooling. The review should show what worked, what remains unresolved and who can authorise the next step.
Rohit
How Pattrn Data helps you build lasting governance
Getting from “we have some flows” to a governed estate you can defend in an audit usually needs a structured first step, not another policy document. Consultancy services include AI risk and efficiency audits, pilot implementations, workflow design, and ongoing managed AI governance and support for firms seeking a Centre of Excellence-style setup without building one from scratch.

A typical audit or pilot leaves you with a workflow map, a risk register, a starter set of DLP and permission policies, and a runbook for the pilot itself, so scaling later is a decision, not a scramble. If your firm handles regulated client data across advice, compliance or document-heavy operations, a governance and workflow controls review is the practical next step. For firms further along, managed managed AI governance and support keep a Centre of Excellence running without adding headcount.
Recommended
Related services
AI governance consulting
Create policies, approval routes, ownership and controls that teams can actually use day to day.
AI governance consultingSecure AI implementation
Put privacy, supplier review, data boundaries, testing and staff guidance into the implementation plan from the start.
secure AI implementationAI workflow automation
Turn repeatable admin, client service and reporting work into controlled workflows with clear human review points.
AI workflow automation support